NAMED ENTITY RECOGNITION APPROACH TO ADVANCED PERSISTENT THREAT IN CYBER THREAT INTELLIGENCE USING BIOAND BILOUTAGGING SCHEME WITH BİLSTM
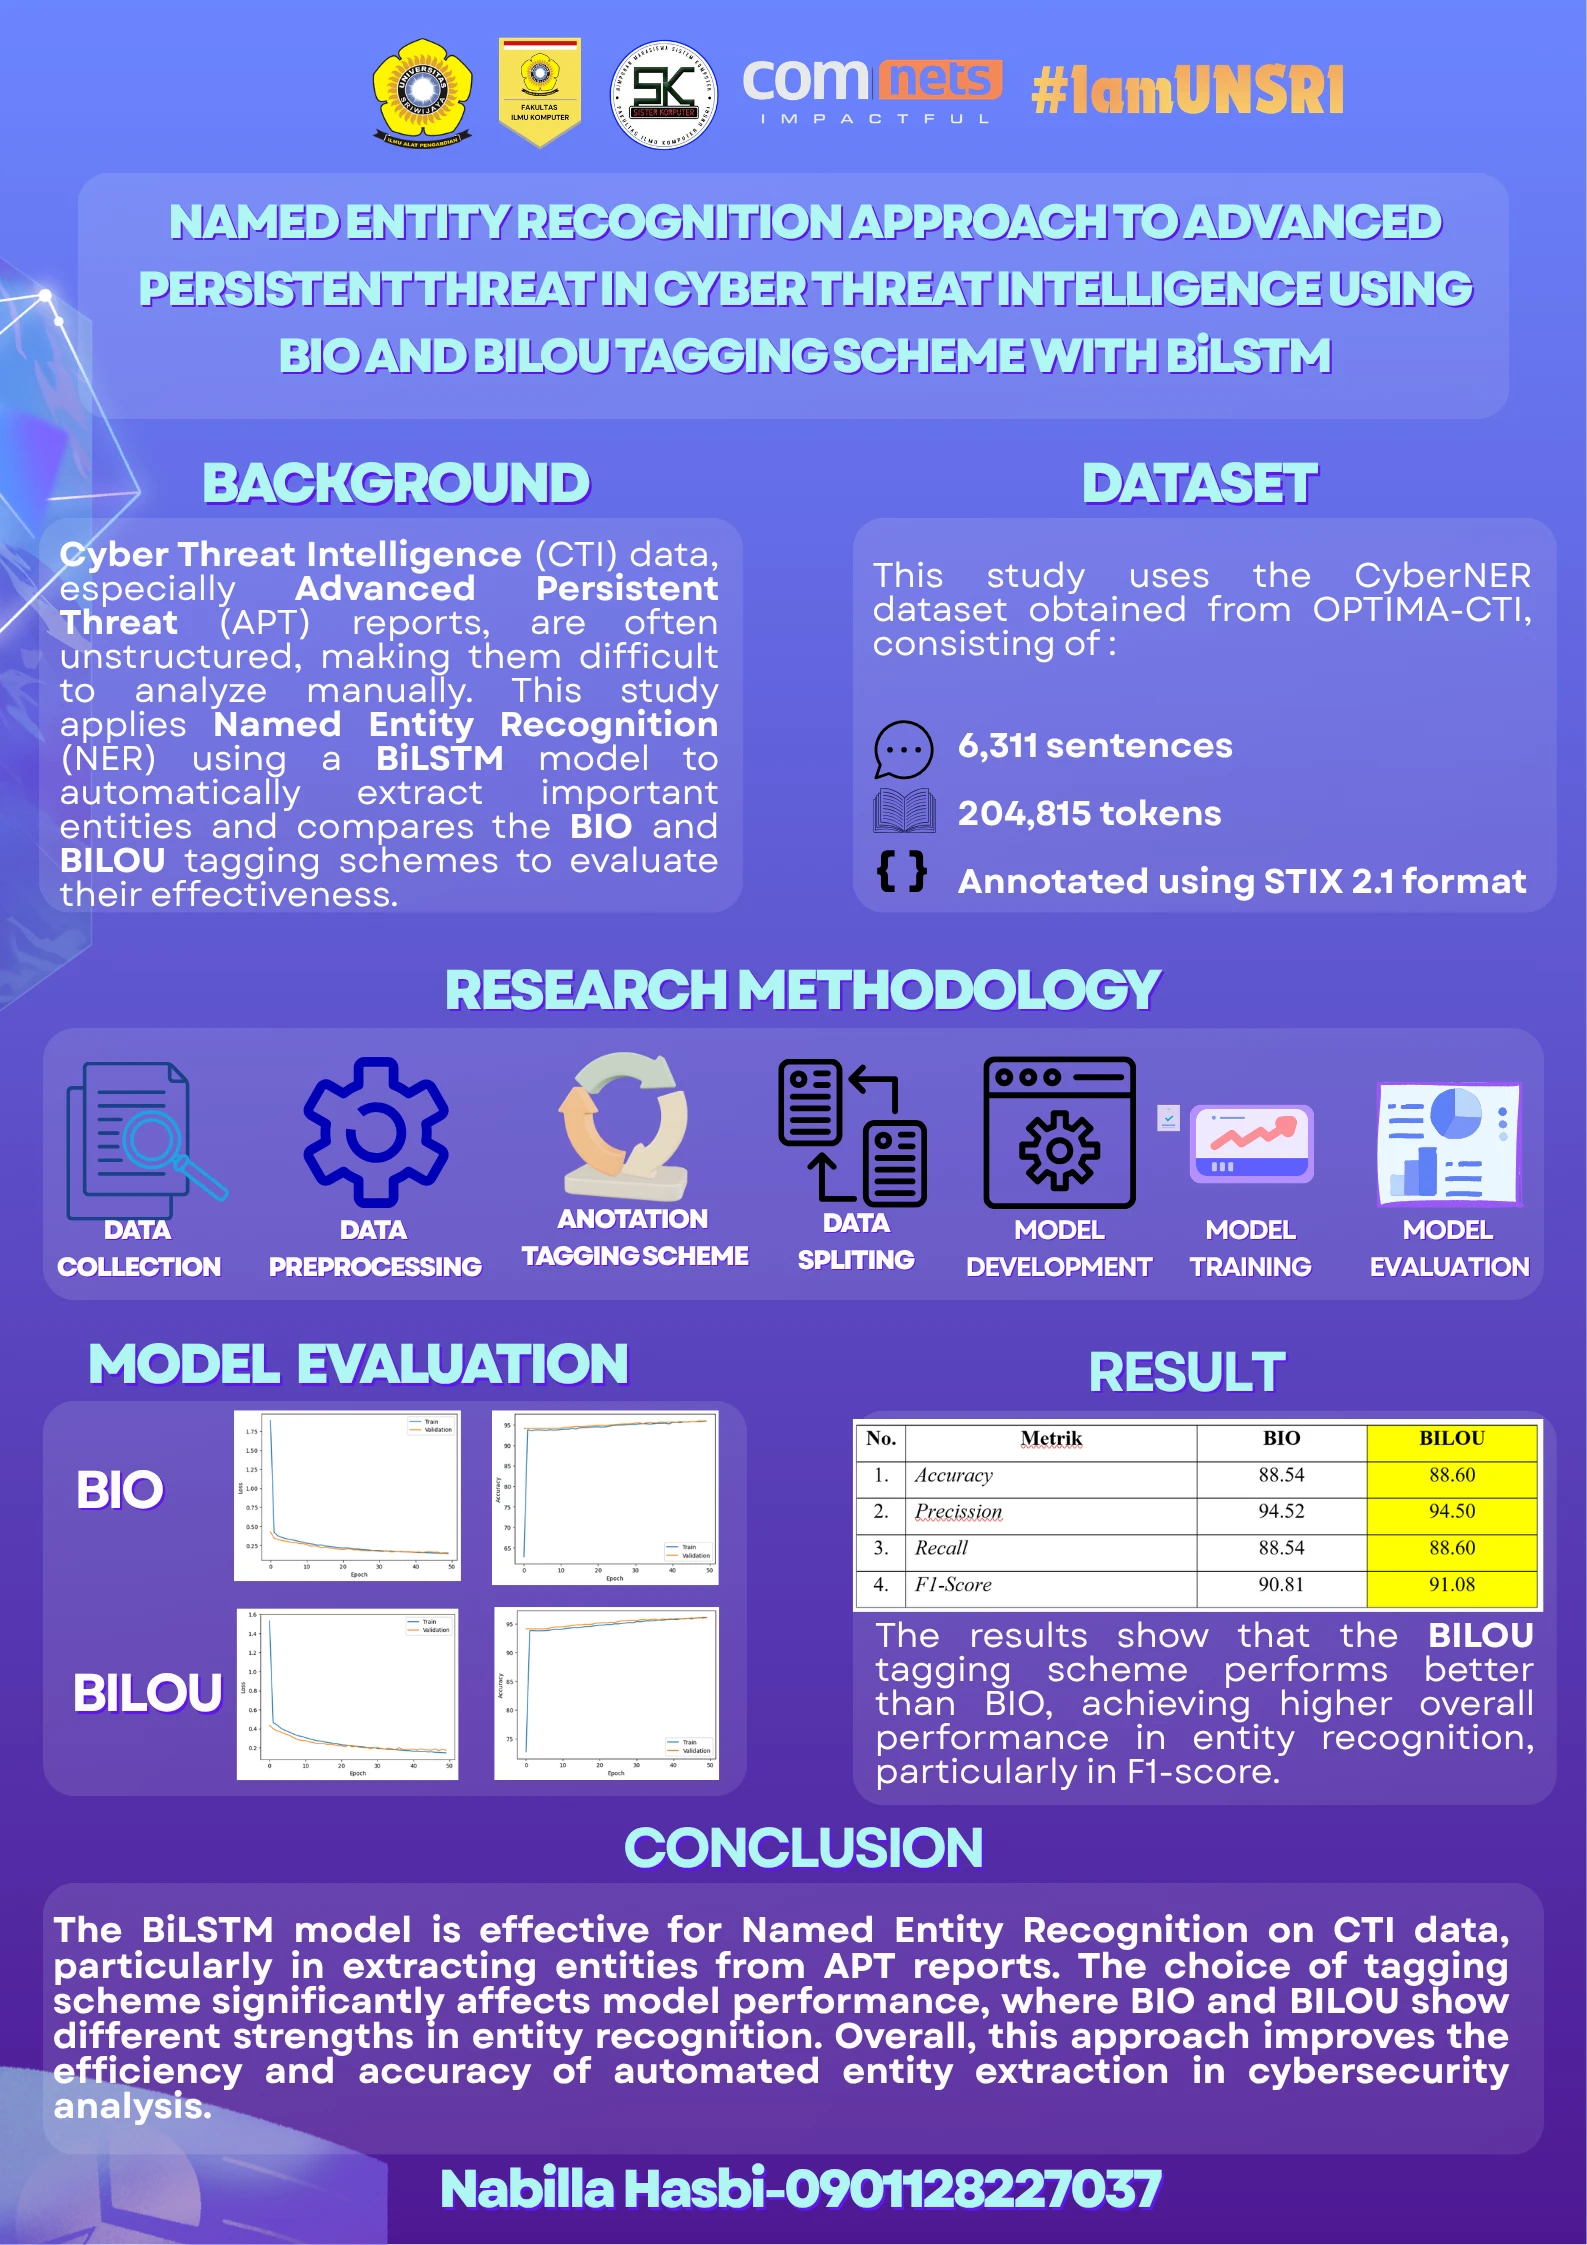
Advanced Persistent Threat (APT) reports in Cyber Threat Intelligence (CTI) are generally presented in unstructured text, making them difficult to analyze manually and requiring automated methods to extract important entities. This study aims to analyze the performance of Named Entity Recognition (NER) using a Bidirectional Long Short-Term Memory (BiLSTM) model by comparing the BIO and BILOU tagging schemes in recognizing entities within APT reports. The dataset used is CyberNER, consisting of 6,311 sentences and 204,815 tokens with 18 STIX entity categories. The research methodology includes data preprocessing, application of BIO and BILOU tagging schemes, BiLSTM model training, and evaluation using accuracy, precision, recall, and F1-score metrics. The results show that BILOU achieves more optimal performance than BIO, with an accuracy of 88.54%, precision of 94.52%, recall of 88.54%, and an F1-score of 90.81%. BILOU also performs better in identifying entity boundaries, resulting in a more balanced precision and recall. Overall, the BiLSTM-based NER approach is effective in extracting important information from APT reports. The choice of tagging scheme significantly affects model performance, where BILOU proves to be more optimal than BIO.
Kreator & Penulis
Nabilla Hasbi
09011282227037