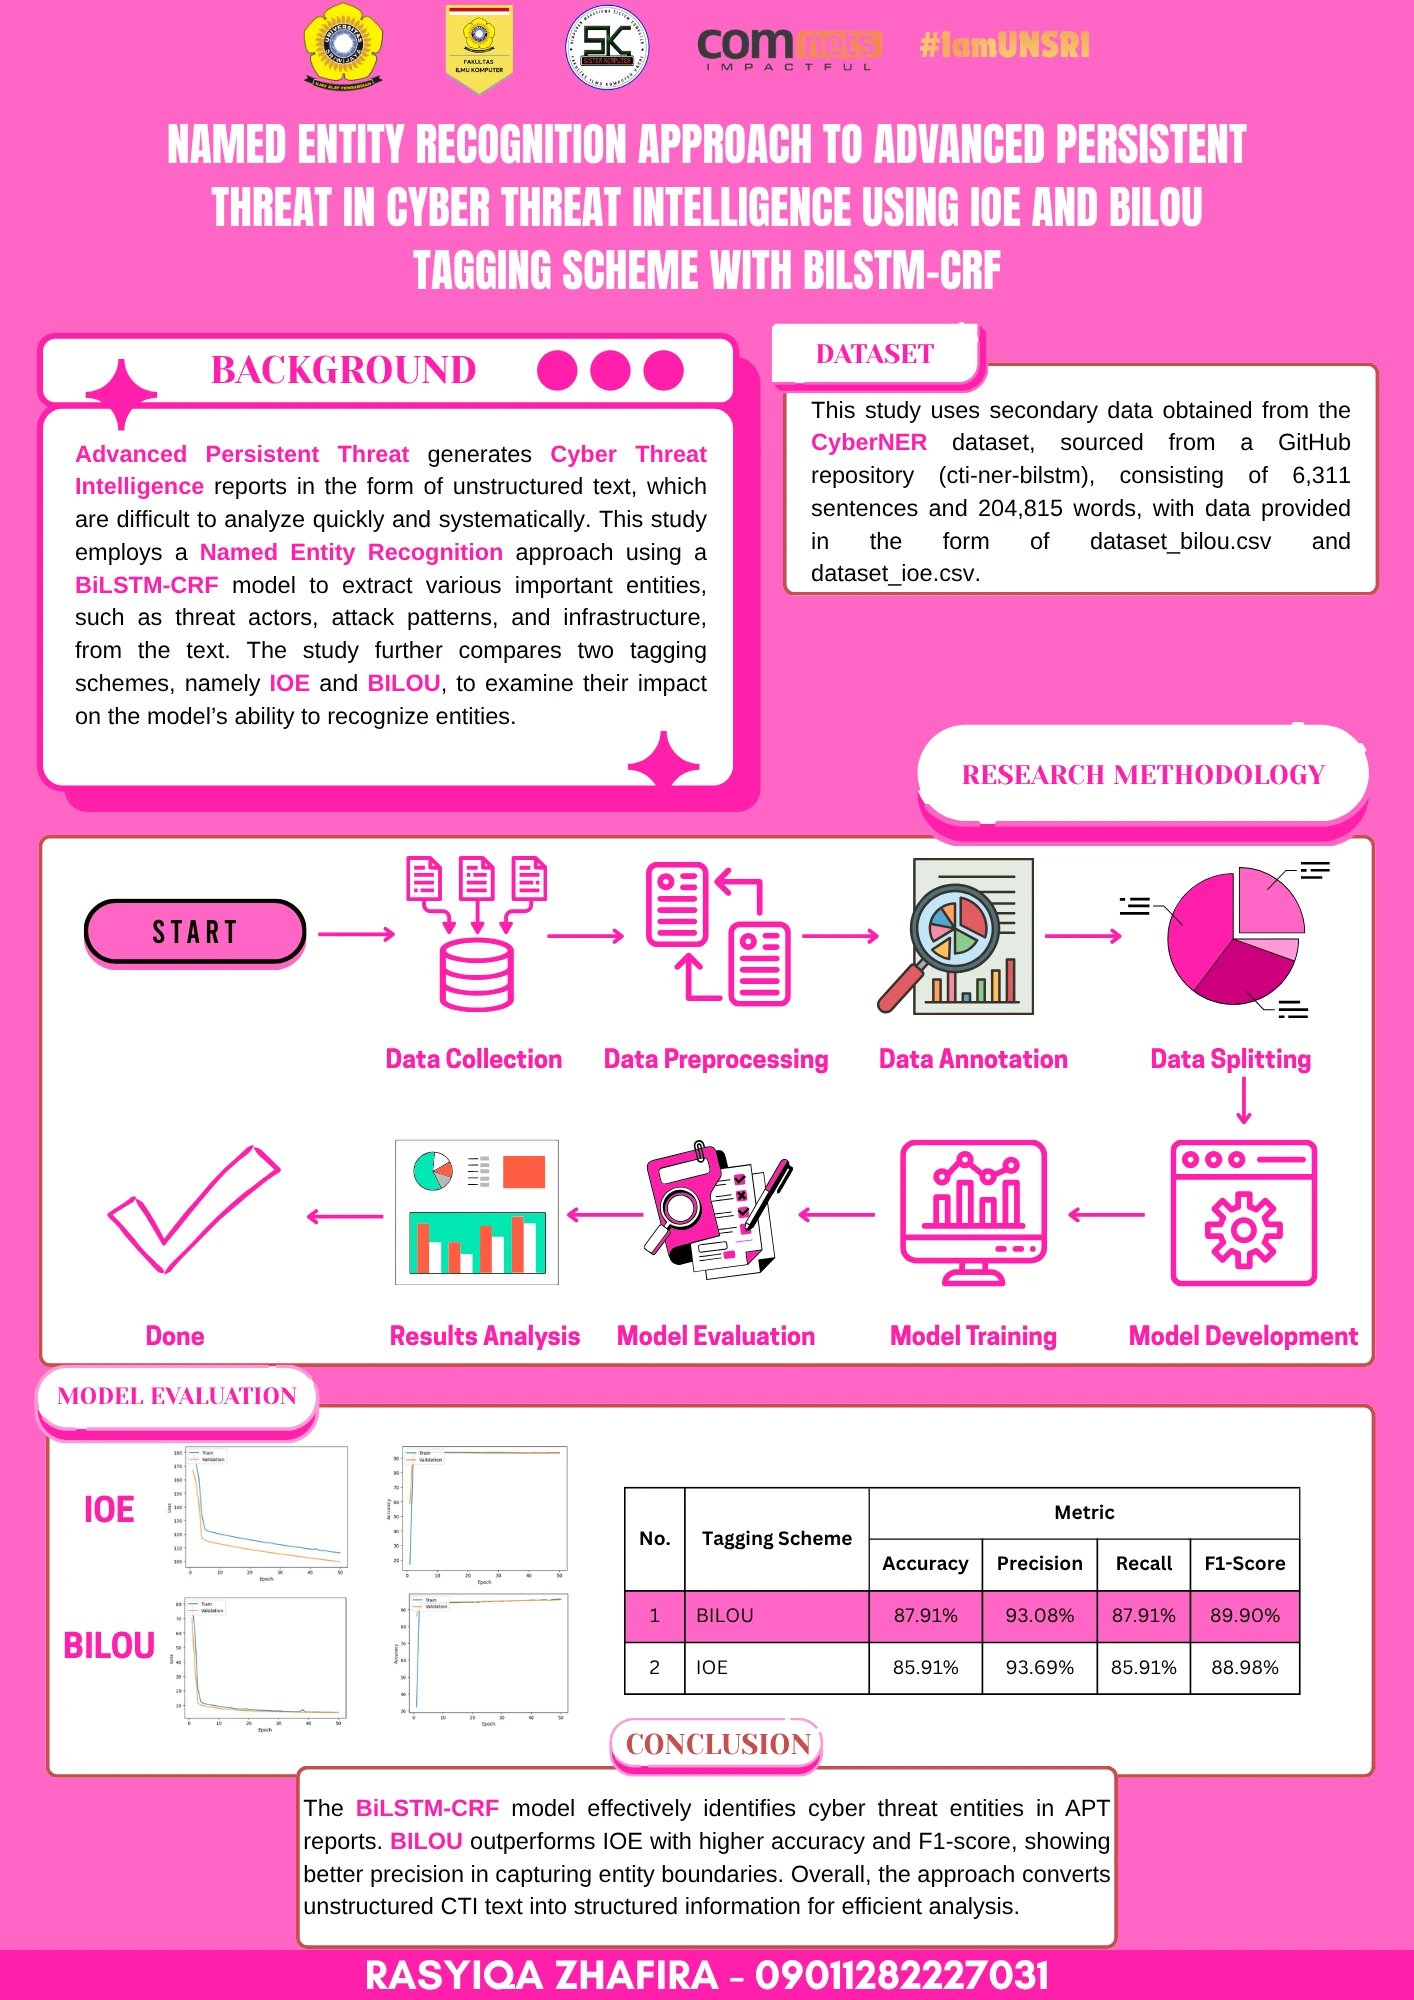
NAMED ENTITY RECOGNITION APPROACH TO ADVANCED PERSISTENT THREAT IN CYBER THREAT INTELLIGENCE USING IOE AND BILOU TAGGING SCHEME WITH BiLSTM-CRF
Advanced Persistent Threat (APT) generates Cyber Threat Intelligence (CTI) reports in the form of unstructured text that is difficult to analyze efficiently. This study aims to extract structured information from CTI reports using the Named Entity Recognition (NER) approach with the Bidirectional Long Short-Term Memory–Conditional Random Field (BiLSTM-CRF) model. The dataset used is CyberNER which consists of 6,311 sentences and 204,815 tokens. The research stages include data preprocessing, annotation using the IOE (Inside–Outside–End) and BILOU (Beginning–Inside–Last–Outside–Unit) schemes, data sharing, training, and model evaluation. Evaluation is carried out using accuracy, precision, recall, and F1-score. The results show that the BiLSTM-CRF model is able to identify cyber threat entities well. The BILOU scheme delivers higher performance with 87.91% accuracy, 93.08% precision, 87.91% recall, and 89.90% F1-score, compared to IOE with 85.91% accuracy, 93.69% precision, 85.91% recall, and 88.98% F1-score. Overall, this approach is able to transform unstructured CTI text into structured information, thus supporting more efficient cyber threat analysis.
Kreator & Penulis
Rasyiqa Zhafira
09011282227031